Imad's Blog

Documenting projects, sharing lessons learned.

Reading Style

AI Moves Into Higher-Stakes Systems, Raising the Bar for Security and Safeguards

AI is becoming less of a standalone tool and more of a layer inside systems where mistakes carry real consequences: medical devices, private messages, government networks and critical infrastructure. This week’s developments point to the same underlying challenge: capability is advancing quickly, but safe deployment depends on controls, monitoring and infrastructure that can withstand failure.

CISA’s red-team assessments expose the importance of response

CISA published lessons from parallel red-team assessments at a government-services organization and a water and wastewater utility. Testers used similar techniques in both environments, but the results diverged sharply.

At one organization, the team achieved domain-level control and reached sensitive systems and cloud resources without an effective intervention. At the other, defenders isolated compromised workstations and stopped suspicious cloud-account activity. Cloud identity and application security appeared repeatedly as weak points, including in environments with capable on-premises detection.

Why it matters: Security products alone do not determine an organization’s outcome during an intrusion. The contrast highlights the value of rehearsed response procedures, clear coordination and the ability to contain suspicious activity across both local systems and cloud services. That is particularly important where business IT is connected to operational technology.

The FDA is preparing guidance for generative-AI medical devices

The FDA says it plans to issue formal guidance for medical devices that use generative AI, along with additional guidance for more specialized or complex applications. An agency discussion paper proposes evaluating systems through demonstrated competencies rather than relying only on conventional measures.

It also considers whether some greater uncertainty before a product reaches the market could be acceptable if it is paired with stronger monitoring after deployment. The FDA is seeking feedback, and some potential monitoring measures may require additional legal authority.

Why it matters: Clinical AI cannot be treated like ordinary consumer software. The emerging framework puts a consequential trade-off in plain view: faster access to potentially useful tools versus stronger evidence that they are safe and perform well in real clinical settings. Post-market monitoring may become central to how that balance is managed.

A reported Taiwan intrusion illustrates how AI agents could lower attackers’ workload

Israeli cybersecurity firm Dream says it found an archive documenting a suspected China-linked intrusion into Taiwanese government networks in early July 2026. According to the report, the operation used as many as eight AI agents in parallel to map systems, test authentication weaknesses and extract personnel data. It reportedly reached a nuclear safety agency and organizations in the energy sector.

Taiwan’s Ministry of Digital Affairs reportedly confirmed an AI-assisted attack on government agencies. Researchers characterized the operation as near-autonomous, rather than entirely free of human involvement.

Why it matters: The important shift is not that an AI system acted wholly alone. If the account is independently substantiated, it suggests agent tools can reduce the hands-on effort needed for reconnaissance and adaptation during an intrusion. That could make sustained, adaptive attack campaigns more accessible to operators who previously needed greater technical skill or staffing.

Actively exploited Oracle and Gitea flaws demand prompt attention

CISA added two vulnerabilities to its Known Exploited Vulnerabilities catalog, a designation based on evidence that attackers are already exploiting a flaw in the real world.

The first, CVE-2026-21962, affects Oracle HTTP Server and the Oracle WebLogic Server Proxy Plug-in. It is an improper access-control flaw, and a separate report describes it as allowing unauthenticated access to critical data. Organizations should identify affected Oracle servers—especially publicly exposed deployments—and remediate them promptly.

The second, CVE-2026-60004, is a code-injection vulnerability in Gitea. Organizations operating Gitea should treat the listing as an urgent reason to patch affected systems and review for signs of compromise, particularly when instances are publicly reachable.

Why it matters: A Known Exploited Vulnerabilities listing is more than a routine disclosure: it is a prioritization signal. Internet-facing enterprise software and developer platforms can offer practical pathways into sensitive systems, so confirmed exploitation should move remediation to the top of the queue.

A critical Keycloak flaw puts identity systems in focus

Red Hat and the Keycloak project released patches for a critical password-reset vulnerability in the open-source identity and access-management server. According to the report, an unauthenticated remote attacker could exploit the flaw to take over any account.

Why it matters: Identity services sit at the center of access to many applications. A weakness that enables account takeover in that layer can extend far beyond a single service. The reported lack of an authentication requirement makes quick identification of affected deployments and application of available fixes especially important.

ChatGPT gains access to Apple Messages—with meaningful permissions

OpenAI has introduced an Apple Messages plug-in for ChatGPT that can search message history, analyze conversations, draft replies and, with permission, send or delete messages. OpenAI says the plug-in runs locally, does not create a complete message index and does not upload message content by default.

However, setup requires Full Disk Access. Users can retain a final approval step before a message is sent, or disable that step.

Why it matters: This is a notable move from AI that merely produces text to AI that can act inside a highly personal communications app. Local processing and review prompts are useful protections, but broad device permissions and the option to automate sending make the design of user controls critical. Convenience should not make it easy to lose oversight of what the tool can read or send.

Intel outlines AI hardware for servers, laptops and the edge

At Hot Chips 2026, Intel presented three products intended for AI workloads across data centers, enterprise systems, laptops and edge devices. Diamond Rapids is a next-generation Xeon platform with up to 256 cores, support for high-bandwidth memory, and PCIe Gen6 and CXL 3.0 connectivity.

Crescent Island is an air-cooled inference GPU with up to 480GB of LPDDR5X memory. Wildcat Lake targets mainstream client and edge devices with an integrated neural processing unit rated at up to 17 TOPS.

Why it matters: Intel’s plans show an attempt to compete across the full AI deployment stack, not only in PCs or traditional servers. Memory capacity, energy use and high-speed connections among components are practical constraints that shape whether AI can run economically at scale.

A cable route to Antarctica could improve scientific connectivity

Researchers have found that a 1,600-kilometer undersea-cable route through the Drake Passage to Chile is viable. Such a connection could replace the current practice of physically transporting some Antarctic research data on hard drives.

Why it matters: A reliable, high-capacity link could reduce delays in moving scientific data from remote Antarctic stations and provide stronger communications infrastructure for research. It is a reminder that the usefulness of advanced computing and AI also depends on the less visible networks that carry data in the first place.

Taken together, these stories point to a more demanding phase for technology. AI is moving into regulated, personal and security-critical settings, while attackers and defenders alike are adapting. Progress will depend not only on what new systems can do, but on whether their permissions, monitoring, incident response and underlying infrastructure are ready for the stakes.

Sources

  • CISA
  • Mario | Health Tech
  • Supercharged With AI
  • The Hacker News
  • Intel Corporation
  • Tom's Hardware

Enterprise Software Is an Organizational Change, Not Just an IT Project

When a company decides it needs a new system, the conversation usually starts with the software.

What does it cost? What features does it have? Which vendor is better?

Those questions matter, but I think there is a more important question to ask first:

What are we actually trying to change?

A company might say it needs a new system because reporting is difficult. But the real problem could be inconsistent processes, poor data, departments working differently, or simply that the company has outgrown the way it used to operate.

New software by itself will not fix those problems.

Start With the Problem

Before looking at products, understand why change is needed.

What isn't working today?

What is making people's jobs difficult?

What information is missing?

What would a better process look like?

This sounds simple, but it can completely change the software selection process.

Instead of looking for the system with the longest list of features, you're looking for the system that best supports what the organization actually needs.

Talk to the People Doing the Work

A company-wide system affects a lot of people.

Accounting may use it one way. Operations may use it another way. Managers may depend on it for reports, while employees may use it every day to complete their work.

That means these people should be involved early.

IT can understand the technology, but we don't always see every problem employees deal with in their daily work.

The people closest to a process often know exactly where the problems are.

Understand Before You Fix

In IT, when someone says something isn't working, we normally don't replace everything immediately.

We troubleshoot first.

Organizational change should work the same way.

If reporting is bad, find out why.

If employees are using spreadsheets instead of the current system, find out why.

If two departments handle the same process differently, understand why before forcing everyone into a new system.

Diagnose the problem before prescribing the solution.

Implementation Is More Than Installation

Once a system is selected, another challenge begins.

People have to change how they work.

Some processes may disappear. Others may change completely. Employees may have new responsibilities or need training. There may also be resistance, especially when people have been doing something the same way for years.

This is why organization-wide software should be treated as planned change, not simply a technology installation.

Communication, training, employee involvement, and leadership support can be just as important as the software itself.

Going Live Doesn't Mean You're Done

Getting the new system running is an important milestone, but it doesn't automatically mean the change was successful.

Go back to the original reason for making the change.

Did reporting improve?

Are employees spending less time on manual work?

Is the information more reliable?

Are departments working together better?

Did the new system actually solve the problem?

If not, learn from what happened and make adjustments.

People, Process, and Technology

The more I work with business technology, the more I believe successful change comes down to three things:

People. Process. Technology.

Technology is only one part.

You can buy great software and still have a poor outcome if the organization doesn't understand the problem, involve the right people, or prepare employees for the change.

So before asking:

"Which software should we buy?"

Start by asking:

"What are we trying to improve?"

That one question can lead to a very different—and much better—conversation.

ClientCall is now available on the Apple App Store!

ClientCall is a field-sales CRM designed around the way people actually work in the field.

Field salespeople are constantly moving between customers and locations. They need to keep track of businesses, contacts, visits, notes, opportunities, and follow-ups, but traditional CRMs can add more complexity than a fast-moving field workflow needs.

That’s the problem I wanted ClientCall to address.

ClientCall provides a focused place to organize businesses and contacts, track visits and activities, manage follow-ups, and see upcoming visits and nearby businesses while you’re out in the field.

Privacy was also an important part of the design.

ClientCall syncs data through the user’s own private iCloud account, without requiring another ClientCall account or separate cloud database.

The goal is simple: give people in the field the CRM tools they actually need without turning the experience into another complicated enterprise system.

Getting ClientCall from an idea to development, testing, Apple review, and now live on the App Store is an exciting milestone.

Version 1 is only the beginning.

If you work in field sales, business development, account management, or regularly visit customers, I’d love for you to try ClientCall and share your feedback.

ClientCall — now available on the App Store.

AI, Infrastructure, and the Systems We Depend On

Technology is becoming more consequential in places where mistakes have physical, legal, or human consequences. This week brought a warning about threats to industrial equipment, new safeguards and surveillance questions around teen AI use, and evidence that some bold claims about autonomous AI research remain premature. Elsewhere, improvements to satellite data delivery and operating-system support show how less visible engineering work can make established systems more useful.

U.S. agencies warn of threats to Siemens industrial controllers

CISA, the NSA, FBI, Department of Energy, and EPA issued a joint advisory about activity targeting Siemens S7 programmable logic controllers, or PLCs, across U.S. critical-infrastructure sectors. PLCs are the specialized computers used to control industrial processes.

According to the advisory, attackers are using internet scanning to find exposed controllers and AI-generated exploitation scripts disguised as monitoring tools. A successful compromise could disrupt operations, damage equipment, create safety risks, and expose sensitive information.

Why it matters: This is not simply a data-security problem. Industrial controllers can be part of energy, water, manufacturing, food production, and other systems with direct effects in the physical world. The agencies’ recommended priorities are clear: keep PLCs off the public internet, apply patches, improve access controls, and watch for unauthorized activity.

OpenAI reportedly adds a teen ChatGPT experience

OpenAI has reportedly introduced a ChatGPT experience for users aged 13 to 17 with stricter limits on discussions of self-harm, romantic and sexual topics, and suggestions that the chatbot has feelings or consciousness.

The service reportedly estimates whether an account belongs to a minor using behavioral signals, including the questions asked, account age, and patterns of use, then applies teen settings automatically. Parents can set quiet hours and receive expanded alerts for high-risk situations.

Why it matters: This is a move away from a single, uniform chatbot experience toward one tailored to inferred characteristics of the user. That may offer stronger protections for young people, but it also makes the accuracy of behavioral age estimation, the privacy implications of that analysis, and any way to challenge an incorrect classification important questions.

AI-designed drugs meet a human-inventor requirement

AI drug-discovery companies can describe molecules as AI-generated, but U.S. patent applications still must identify human inventors. A 2022 U.S. appeals-court ruling held that an inventor under the relevant statute must be a human individual.

That leaves companies using AI for molecular design needing to show that people made sufficient inventive contributions, even when AI played a substantial role in identifying or shaping the compound.

Why it matters: Patent protection can determine whether developers can commercialize expensive drug research. As AI becomes more capable in scientific workflows, the gap between its practical contribution and the law’s definition of an inventor may create uncertainty—and potential challenges—for future drug patents.

Faster satellite data for wildfire responders

The European Space Agency and Eumetsat have changed how Copernicus Sentinel-3 satellite data is transmitted to ground stations. ESA says the change allows emergency services to receive the data up to three times faster, supporting quicker responses to wildfires across Europe.

The improvement comes from changes to the ground-data system rather than a new satellite.

Why it matters: Observing a fast-moving fire is only useful if the resulting information reaches people making decisions in time. This is a practical reminder that the value of a satellite system depends not only on what is in orbit, but also on the networks and operations that turn its observations into usable information.

AI agents still fall short on open-ended research

A study cited by MIT Technology Review finds that current AI agents cannot yet carry out open-ended AI research, where progress relies on judgment and creativity rather than finding a predefined answer.

The result challenges near-term claims that AI systems will be able to improve themselves autonomously with little human oversight. At the same time, it does not rule out meaningful progress from AI systems working on narrower research tasks.

Why it matters: Predictions of rapid recursive self-improvement depend on systems being capable of more than completing well-scoped assignments. This finding is a useful empirical counterweight to sweeping forecasts, while leaving the longer-term question unresolved.

The search for naturally occurring hydrogen

Interest is growing in geologic hydrogen: hydrogen produced naturally underground when water reacts with iron-rich rocks. Exploration is underway in the U.S. Midwest and elsewhere. HyTerra reports samples containing up to 96% hydrogen in Nebraska and Kansas.

Researchers are also testing ways to stimulate hydrogen-producing reactions in subsurface rock. Commercial viability, however, remains unproven.

Why it matters: If recoverable at useful volumes and costs, geologic hydrogen could be an alternative to hydrogen made from fossil fuels. But major practical questions remain, including production rates, capture, storage, transport, and whether the approach can scale.

Linux kernel 7.2 broadens support for newer hardware

A new Linux kernel point release adds HDMI 2.1 support for AMD Radeon hardware and lets Apple M3 MacBooks boot Linux for the first time. It also turns on Btrfs large-folio support by default, changing how that filesystem handles larger memory pages.

Why it matters: Kernel support is what makes hardware reliably usable on Linux. Better support for modern Radeon graphics and Apple Silicon laptops can remove practical barriers for people who want to run Linux on newer machines, even if these changes matter most to a relatively technical group of users.

Epic faces scrutiny alongside questions about its AI plans

Epic Systems presented its product roadmap at its annual customer meeting while facing antitrust lawsuits, state and federal inquiries into its business practices, questions about its AI strategy, and departures of key technology leaders.

STAT reports that Epic holds at least one health record for 82% of Americans, though the available newsletter summary offers limited detail on its announcements and the investigations.

Why it matters: Electronic health-record systems are foundational infrastructure for hospitals, clinicians, and patients. Epic’s decisions about AI, data access, and competition could therefore have effects far beyond one company or its annual meeting.

Telegram bots reportedly reward deepfake sexual-image abuse

Cybernews reports that Telegram bots are being used to generate non-consensual deepfake pornography targeting women and children. Some of the bots reportedly reward repeat users, suggesting their design may encourage repeated abuse.

The available report does not provide details about the rewards, the bots’ operators, the scale of the activity, or Telegram’s response.

Why it matters: Generative AI can reduce the effort required to create and distribute sexual-image abuse. If systems are structured to reward repeated use, that design could compound the harm to victims and increase the need for effective platform moderation and enforcement.

Hubble data adds to the Milky Way’s early history

NASA says data from the Hubble Space Telescope provides evidence that a dwarf galaxy merged with the young Milky Way. The result adds detail to the established picture of the Milky Way growing through the absorption of smaller galaxies.

According to NASA, the evidence extends the known history of the galaxy’s evolution 1.8 billion years further back than previous evidence.

Why it matters: The finding helps explain how the galaxy around us took shape. It is also a useful reminder that familiar objects in the night sky still contain a deep, discoverable history.

The common thread is not that AI is replacing every system around it. It is that AI is being introduced into systems with very different stakes—from industrial controls and health records to scientific research and consumer services. The important work is increasingly in the details: security boundaries, legal accountability, timely data, and safeguards that hold up in real use.

Sources

  • CISA
  • Supercharged With AI
  • The Checkup from MIT Technology Review
  • ESA
  • The Download from MIT Technology Review
  • The Spark from MIT Technology Review
  • Abhi from It's FOSS
  • STAT
  • Cybernews
  • NASA

AI’s Growth Is Testing the Systems Around It

AI’s expansion is increasingly a story about the systems around the models: the power plants and financing behind data centers, the software frameworks that give agents real capabilities, the security of distributed-computing deployments, and the public safeguards governing data collection.

This week’s developments also offer a reminder that scale alone is not the measure of progress. Whether a system is useful, safe, or accountable depends on how it is financed, operated, secured, audited, and understood.

Flock’s license-plate search safeguards still leave major questions

Flock Safety, which operates roughly 120,000 automated license-plate readers in the United States, has added safeguards intended to reduce misuse of its police-search platform. Officers must now enter a case number before conducting a search. But Flock does not verify that number.

That distinction matters. The Washington Post identified 50 misuse cases involving Flock and competing systems, often involving stalking or harassment. Agencies can also retain vehicle-location data for months or years.

Why it matters: Automated plate readers can be useful in investigations, but their ability to search across jurisdictions creates the potential for a broad location-surveillance network. A required field is not a meaningful control if no one verifies it. Effective safeguards would require enforceable sharing limits, short retention periods, auditable emergency access, and real verification of why a search is taking place.

Nvidia reportedly backs financing for a huge Ohio AI campus

Nvidia is reportedly supporting about $105 billion in financing tied to OpenAI’s planned 20-year lease for a 10-gigawatt data-center campus in Pike County, Ohio. SB Energy, a SoftBank power subsidiary, would build and operate the site. Nvidia’s reported support would cover construction and lease costs, rather than the chips themselves.

The Neuron estimates the full project, including chips, could exceed $500 billion. The arrangement remains reported rather than confirmed in the supplied material.

Why it matters: The proposed campus illustrates the extreme capital and electricity requirements associated with frontier AI. It also points to a tighter web of relationships among AI labs, chip companies, power providers, developers, and financiers. If this arrangement proceeds, Nvidia’s role would extend beyond supplying hardware to OpenAI.

CISA flags four actively exploited flaws in widely used products

CISA added four vulnerabilities to its Known Exploited Vulnerabilities catalog after finding evidence that they are being actively exploited. The affected products include Microsoft IKE service extensions, Microsoft SharePoint, Broadcom VMware vCenter, and Apple macOS.

Why it matters: A routine patch notice can wait behind other work; evidence of exploitation changes the calculation. Organizations should determine whether these products are present in exposed or critical parts of their environments and prioritize the relevant updates or mitigations. CISA recommends a risk-based approach, which means considering exposure and operational importance rather than treating every update identically.

An actively exploited Ray flaw puts AI infrastructure on notice

CISA also added CVE-2025-62593, a code-injection vulnerability in Ray-Project Ray, to its Known Exploited Vulnerabilities catalog. A separate report described the issue as capable of browser-based remote code execution.

Ray is an open-source platform used to build and run distributed-computing and AI workloads. Organizations using it should identify exposed deployments and apply the project’s guidance.

Why it matters: AI systems depend not only on models, but also on an expanding stack of orchestration and distributed-computing software. A flaw in that layer can be as operationally important as a flaw in a conventional server platform. CISA’s active-exploitation finding makes this a current security priority, not a deferred maintenance task.

Medusa ransomware continues to target critical sectors

CISA, the FBI, and the Department of Health and Human Services updated their joint advisory on Medusa, a ransomware-as-a-service operation first identified in 2021. As of April 2026, the advisory says Medusa had affected more than 500 victims across health care, manufacturing, government, IT, and financial services.

The group gains access through access brokers, phishing, and newly disclosed but unpatched internet-facing vulnerabilities. It then uses legitimate tools and remote-access services to move through networks, steal data, and encrypt systems.

Why it matters: The advisory reinforces some familiar but essential practices: patch internet-facing systems promptly, restrict remote services, and segment networks. Medusa also uses double extortion, meaning attackers may steal data as well as encrypt it. In that situation, restoring from backups alone does not necessarily resolve the incident’s consequences.

DeepSeek open-sources an agent runtime built for reversible capabilities

DeepSeek Harness is presented as an MIT-licensed framework for the software surrounding an AI model: tools, memory, execution, storage, scheduling, sandboxes, and interfaces. Its central idea is to treat capabilities as plugins, including temporary plugins that an agent can create, load with permission, use, and remove.

An accompanying architecture called Cordis is intended to manage dependencies and reversible effects when services disappear or change.

Why it matters: As AI models become easier to swap, the surrounding runtime may become the more important layer. It determines what a model can access, what it remembers, which permissions it receives, and how its actions are controlled. An open framework could offer developers an alternative to proprietary agent environments, though its reliability in real-world deployments remains unproven.

Independent measurement may reveal a different picture of AI use

A new research project, the AI Observatory, argues that public usage reports from companies provide only a selective view of how people use systems such as ChatGPT, Claude, and Gemini. Its analysis reportedly found more sensitive and personal use than company reports emphasize, along with different dominant patterns by model: coding with Anthropic, social and roleplay use with Gemini, and homework help with ChatGPT.

Why it matters: Decisions about AI’s benefits, risks, and safeguards depend on knowing how people actually use it. Company-published data can be useful, but it may not fully capture private or sensitive activity. Independent measurement could make such claims easier to scrutinize and better ground policy and product decisions in observed use rather than selective reporting.

Closing perspective

The common thread is that the consequential questions around AI are no longer confined to model performance. They involve power and capital, software dependencies and patching, privacy boundaries, and the quality of public evidence. Building capable systems is only part of the task; operating them responsibly requires durable infrastructure and safeguards that can be checked in practice.

Sources

The Algorithm from MIT Technology Review

The Neuron

CISA

The Hacker News

Turing Post

The Download from MIT Technology Review

STEM Feed Is Officially Live on the App Store

STEM Feed Is Officially Live on the App Store

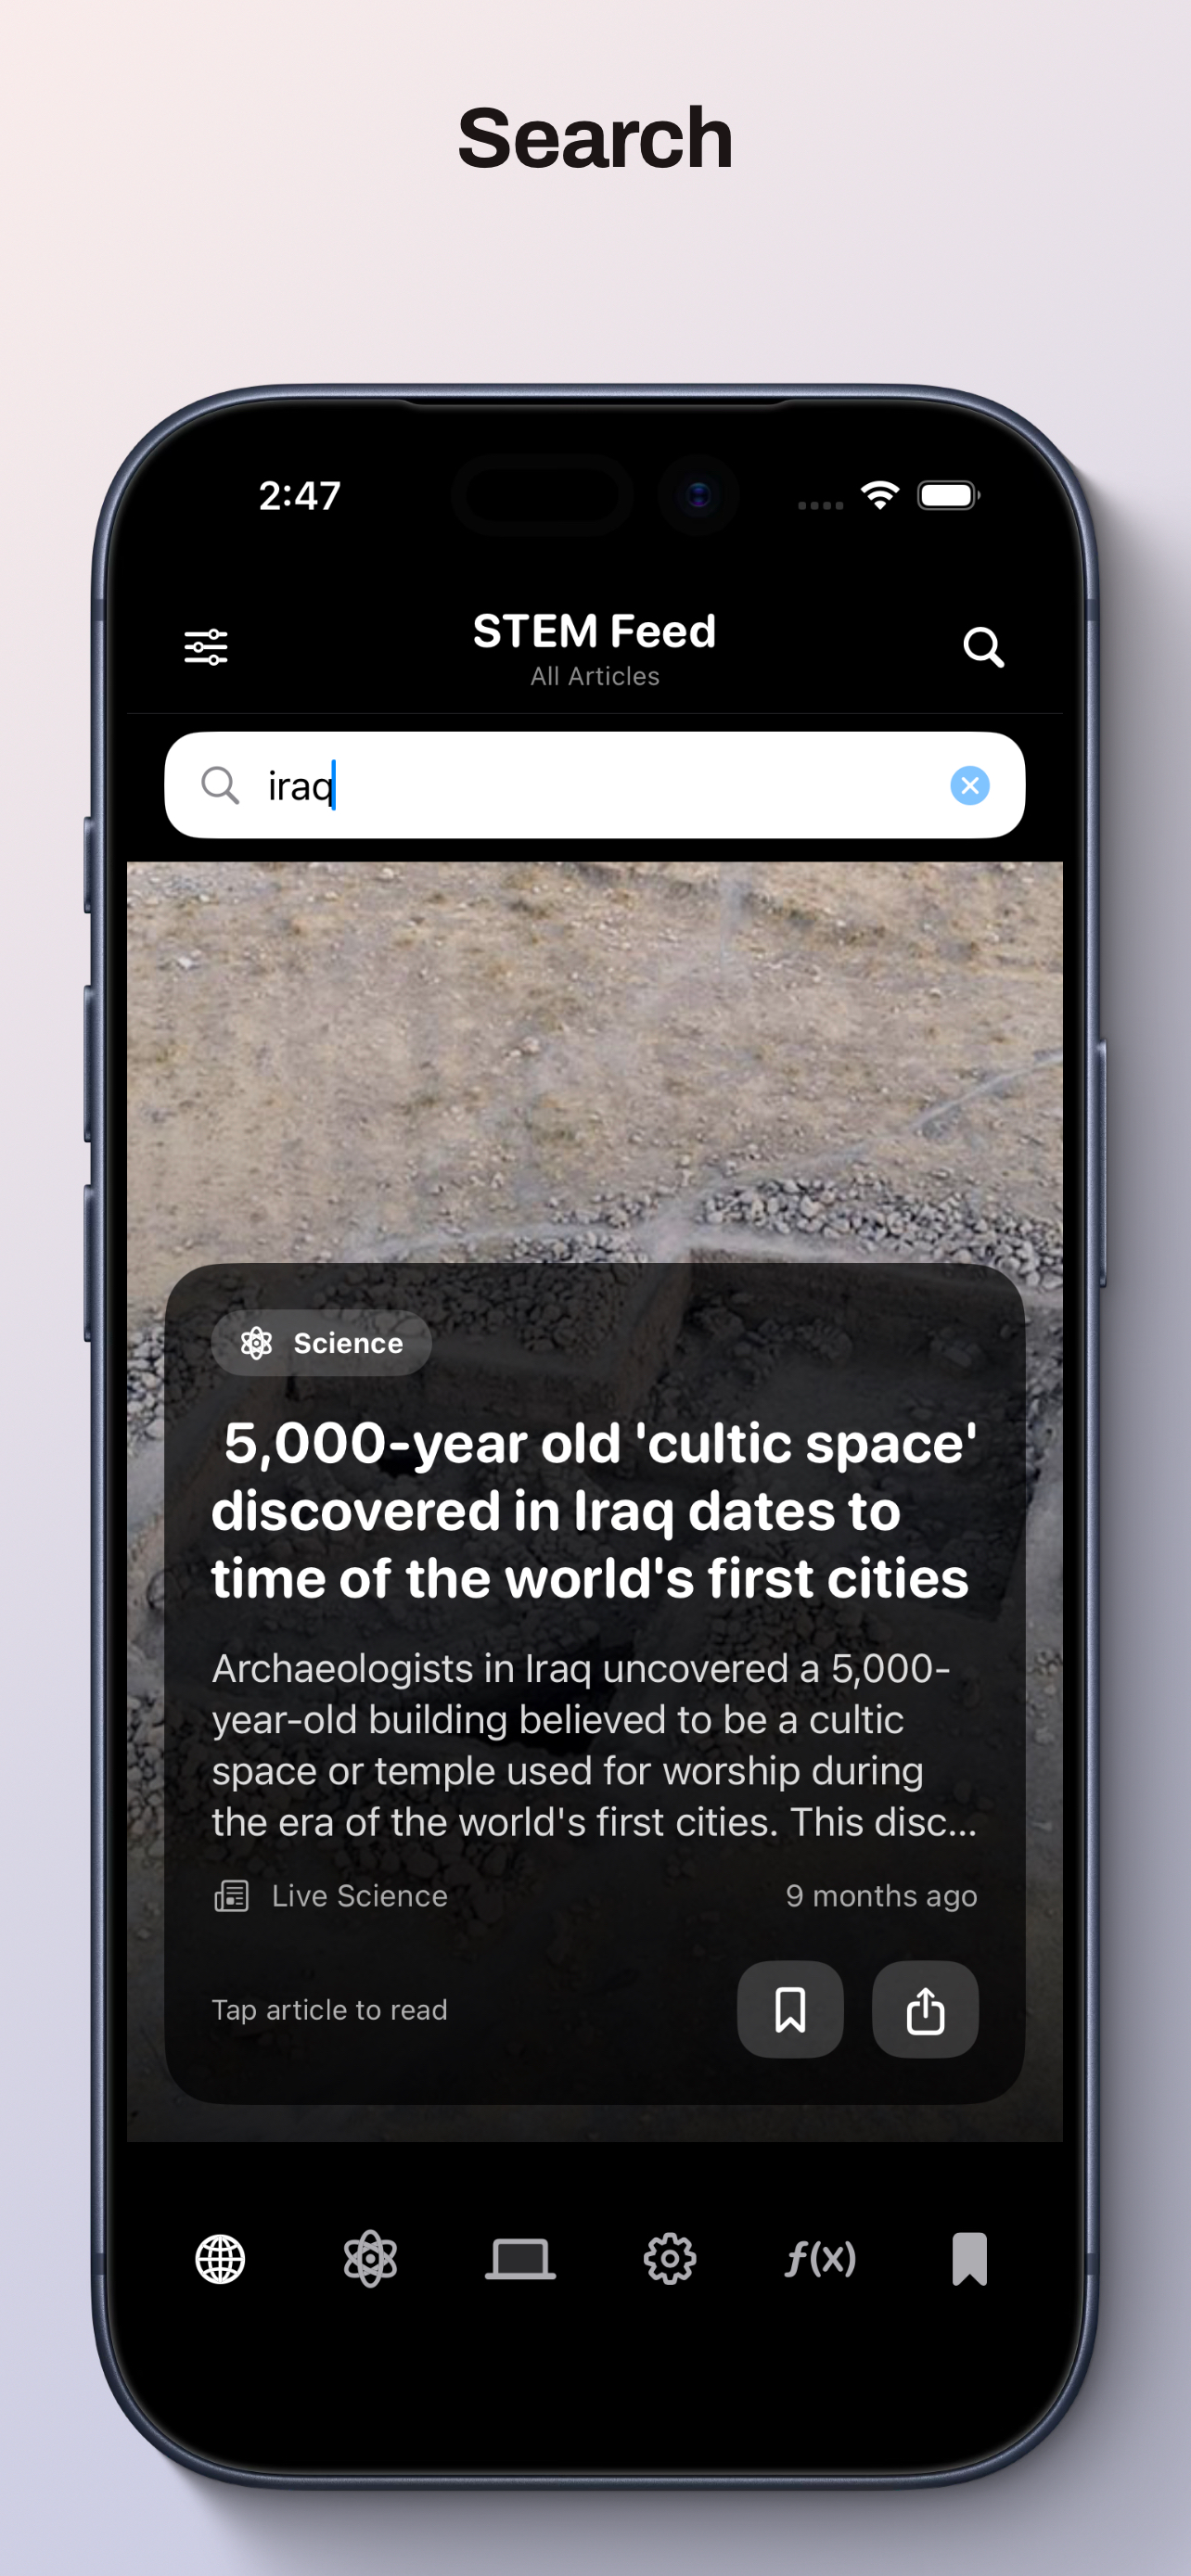
I’m excited to share that STEM Feed is officially available on the Apple App Store.

STEM Feed is an iOS app built around a simple idea: creating a focused feed for discovering and exploring STEM-related content.

A major part of building STEM Feed has been thinking beyond simply displaying content. The goal is to continually improve how the feed feels—how content is selected, varied, presented, and discovered—while keeping the experience fast, simple, and respectful of user privacy.

A Different Approach to the Feed

The feed is the heart of STEM Feed.

Instead of overwhelming the experience with unnecessary features, STEM Feed focuses on making it easy to open the app and start discovering interesting STEM content.

Behind that simple experience is an ongoing effort to improve feed quality, content variety, performance, and recommendations.

Privacy-Conscious by Design

As STEM Feed evolves, personalization will be approached with privacy in mind.

Future versions will explore ways to make feeds more relevant and varied without requiring unnecessary personal information. The goal is to improve discovery while keeping the experience lightweight and privacy-conscious.

Version 1 Is Just the Beginning

Getting STEM Feed through development, testing, App Store review, and finally into the hands of users is an exciting milestone.

But this release is the foundation.

There is plenty more planned for STEM Feed, particularly around feed intelligence, discovery, personalization, and the overall user experience. Feedback from real-world use will help shape those improvements.

For now, I’m excited to finally say:

STEM Feed is live on the App Store.

If you enjoy discovering STEM content and exploring new ideas, check it out and let me know what you think.

More updates are coming.

Image 1 for STEM Feed Is Officially Live on the App Store
STEM Feed Is Officially Live on the App Store — 1 image

Infrastructure Under Pressure: Epic Scrutiny, Active Exploits, and a Spacecraft Update

Technology infrastructure is under pressure on several fronts: competition policy, urgent security maintenance, and the challenge of keeping complex systems operating far from the ground. This week’s developments range from U.S. health-record software to internet-exposed computers and a spacecraft preparing for a delicate orbital operation.

FTC examines Epic Systems’ business practices

According to STAT, the Federal Trade Commission is examining Epic Systems, the largest U.S. electronic-health-record vendor, for potential antitrust-law violations. The inquiry is described as a broad review of the company’s business practices, and investigators have recently contacted people familiar with the matter.

The scale of Epic’s role makes the inquiry significant. STAT reports that roughly 82% of Americans have at least one record stored in Epic systems. Electronic health records are not simply back-office software: they are core infrastructure for hospitals and clinical care.

Why it matters: Any scrutiny of a company with such a large presence in health care could have consequences for competition, the ability of different systems to exchange information, and how easily providers can choose or change vendors. At this stage, the supplied reporting describes an inquiry, not a finding of wrongdoing.

Exploitation attempts follow patches for SAP Commerce and macOS

Attackers are reportedly attempting to exploit CVE-2026-58231, a maximum-severity vulnerability in SAP Commerce Cloud, only days after a patch was issued. Separately, the Netherlands National Cyber Security Centre warned that attackers are exploiting a patched macOS Screen Sharing flaw on internet-exposed Macs to install Monero-mining malware.

These reports reinforce an uncomfortable reality of security operations: applying a patch is essential, but speed matters once attackers begin targeting a newly disclosed weakness. Systems that are exposed directly to the internet can create a particularly immediate opportunity for attackers.

Why it matters: Organizations running SAP Commerce Cloud and people responsible for internet-exposed Macs should treat the reported exploitation as an urgent reason to patch and reduce unnecessary exposure. The issue is not only the existence of a vulnerability, but the indication that attackers may already be trying to use it.

Katalyst updates LINK ahead of a planned Swift Observatory capture

Katalyst Space has uploaded a flight-software update to its LINK spacecraft, adding attitude-control algorithms intended to stabilize the vehicle using its remaining actuators. NASA says the update is meant to support LINK’s continued approach to the Neil Gehrels Swift Observatory.

The planned next step is ambitious: LINK is intended to attempt to capture the telescope and raise its orbit. The available information is limited on the spacecraft’s condition and on the details of the capture operation, so this remains a progress update rather than evidence that the operation has succeeded.

Why it matters: If successful, the effort would be a meaningful demonstration of servicing an existing spacecraft in orbit. It also illustrates the distinctive engineering challenge of maintaining a complex vehicle after launch, where software updates may be one of the few available ways to adapt to changing conditions.

Across health care, cybersecurity, and space operations, the common thread is the importance of systems that are difficult to replace, difficult to maintain, or both. Regulatory scrutiny can test how infrastructure markets operate; active exploitation tests how quickly operators can respond; and orbital servicing tests whether vital hardware can be sustained beyond its original design assumptions.

Sources

  • STAT
  • The Hacker News
  • NASA
All websites and desktop applications shown here are intended for personal or light business use. For production-level or custom business software, please contact me directly.